Set Network Settings for Clients and Outbound Traffic
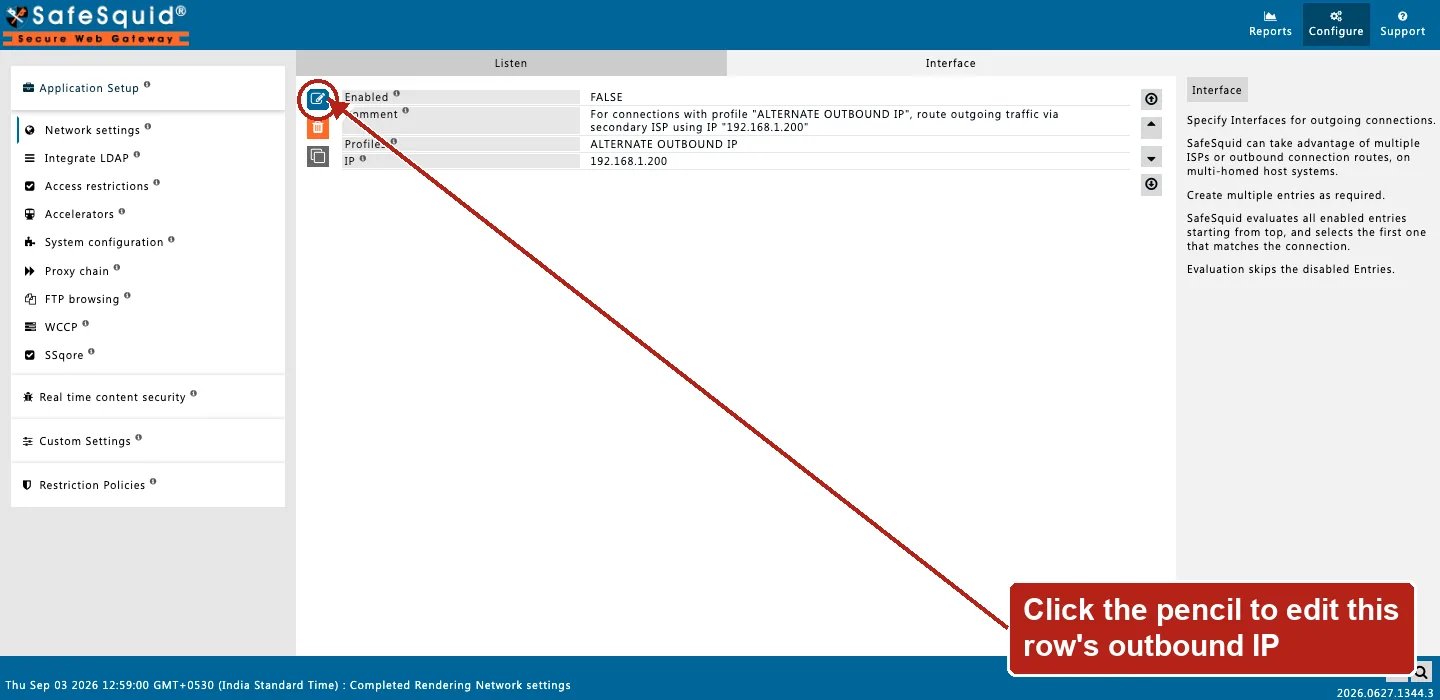
The Network section defines client listen sockets and outbound source IP selection for origin connections. The console splits this section into two tabs, and they are independent of each other: Listen binds the sockets clients connect to, Interface picks the source IP SafeSquid uses when it connects onward. These are infrastructure-plumbing settings, not a security control in themselves: Listen decides where clients may knock, and Interface decides which door SafeSquid walks out of. Who is allowed in, and what they may do, belongs to Access restrictions, which references the Listen sockets defined here through its own Interface match field. Nothing can reach SafeSquid at all unless a Listen entry is bound.- Listen
- Interface
Core mechanics
Listen — startup bind
Every enabled Listen row withport != -1 binds at startup. If no enabled row matches startup.ini LISTEN_IP and LISTEN_PORT, an additional fallback bind runs on those defaults. This fallback is extra, it does not replace or disable any entry you configured. It only fires when nothing in your list already covers that address. Restart required after Listen changes.Listen fields
Open Configure → Application Setup → Network settings → Listen.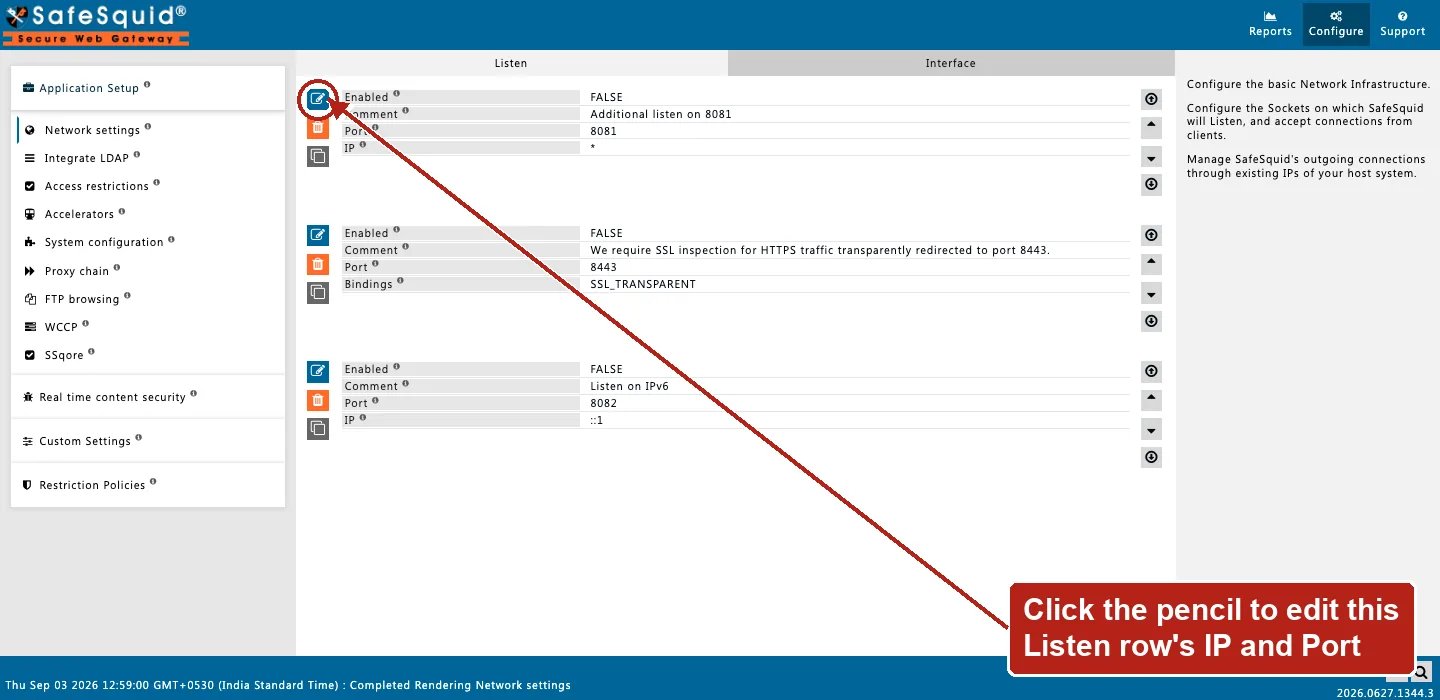
Network settings — Listen rows
- IP / Port — Bind address and client port. Blank IP binds every address dual-stack where IPv6 is available;
0.0.0.0binds every IPv4 address;::binds every IPv6 address. A specific address binds only that one. - Bindings —
SSL_TRANSPARENT,CAPTIVE_PORTALimplemented;SSL_AUTHENTICATION/SSL_BRIDGEhave no effect.
Examples
How to verify
- Restart after Listen changes.
curl -x http://APPLIANCE:8080 http://example.com/- Enable NETWORK logs; confirm the bind lines.
- Match listen socket in Access Interface for CONFIG vs PROXY tests.
Next steps
- Access restrictions - define who can connect through SafeSquid, whether they must authenticate, and which proxy features they get, using ordered first-match rules.