Problem
Security teams need predictable control over app and web usage to reduce policy bypass and data-risk exposure.Benefits
You can enforce policy decisions consistently with SafeSquid while preserving legitimate business workflows.Advantages
You keep actionable policy control close to operations, with verifiable outcomes in logs and policy behavior.Call to action
Use the steps in this guide to implement the control, then validate behavior with a real user-flow test.Block Personal Gmail, Allow Google Corporate Accounts
Problem: Personal webmail increases data and productivity risk
Organizations that use Google Workspace need to allow corporate Google accounts while blocking personal Gmail. Personal email on the office network consumes productive time and can create a path for leakage of confidential information. Many organizations use Google Corporate domains for mail; Gmail cannot be blocked entirely. SafeSquid SWG allows only configured corporate domains for Google sign-in and blocks personal Gmail.Key benefits
Corporate Google accounts continue to work for mail and Google services. Personal Gmail sign-in is blocked so users cannot use non-corporate accounts. Policy is enforced via header manipulation so only allowed domains are accepted by Google. Administrators list allowed domains (e.g.corp.example.com) in one place.
Prerequisites
- HTTPS Inspection enabled so SafeSquid can inspect and modify HTTPS traffic to Google.
- Access to SafeSquid Configuration Portal (Configure page).
- List of allowed Google Workspace domains (e.g.
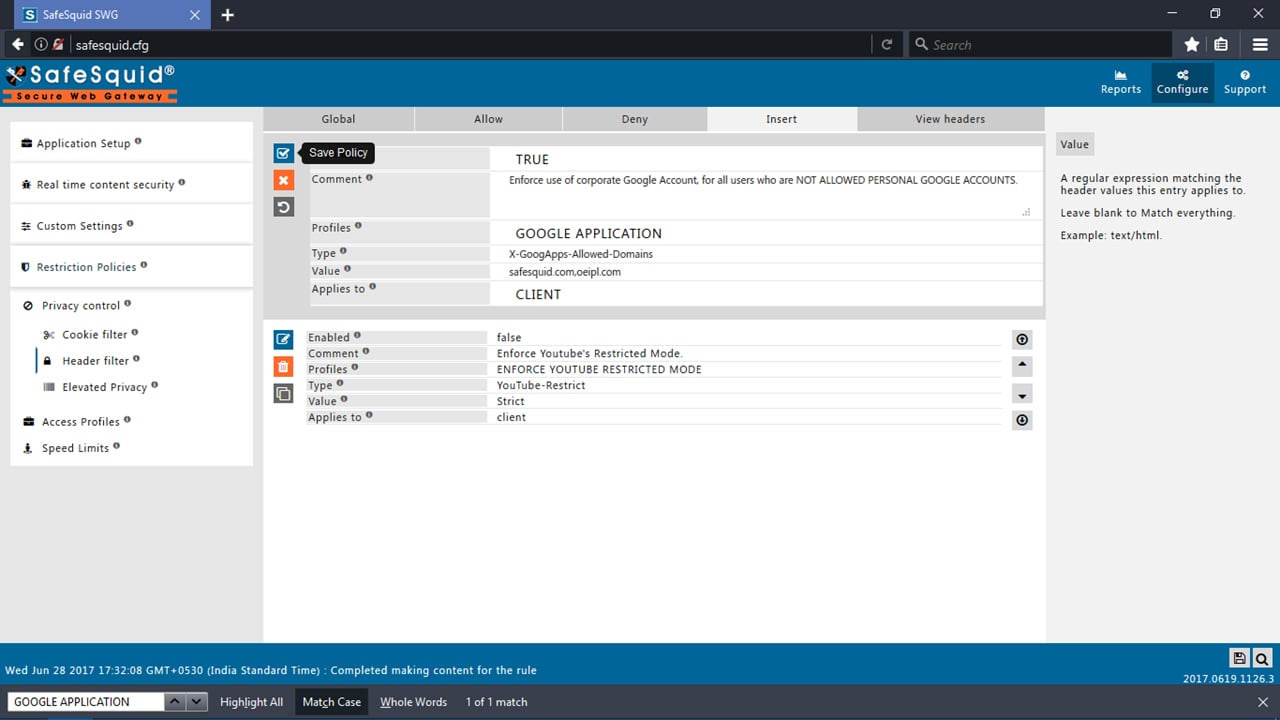
corp.example.com). Multiple domains are separated by comma with no space.
Call to action
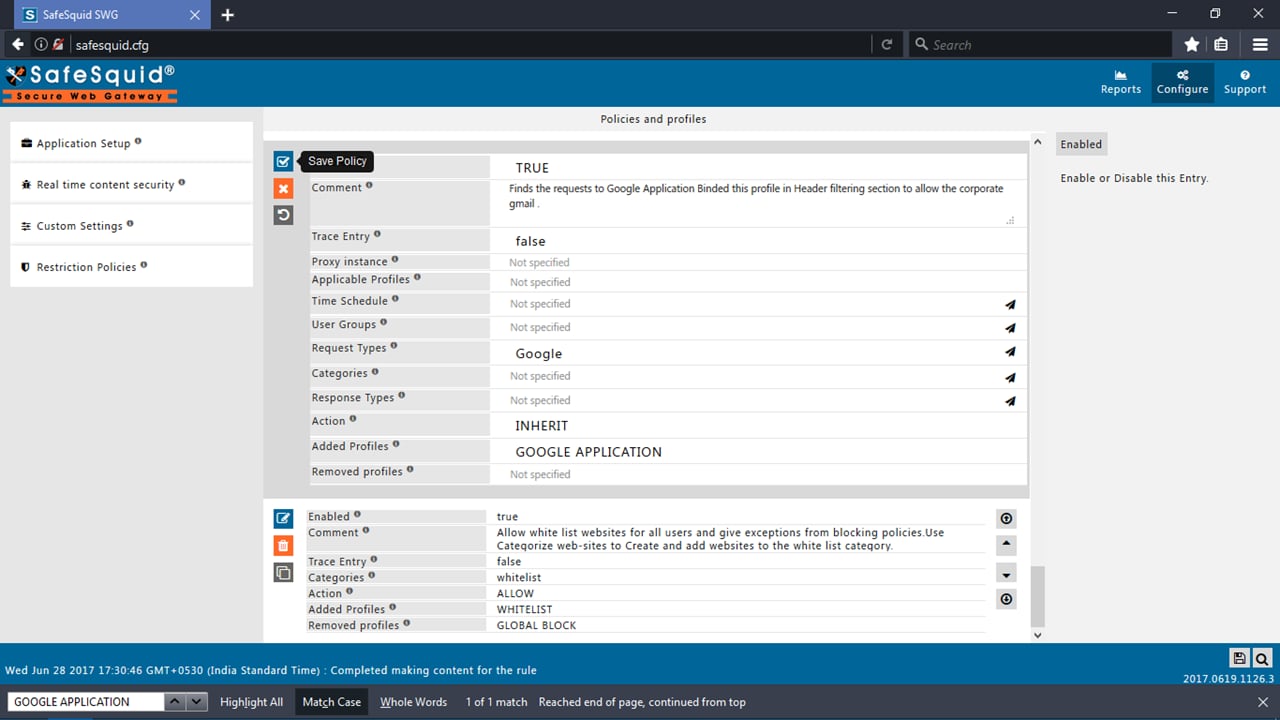
Enable policy from Policies and Profiles section
Match requests to the Google Application policy first.- From SafeSquid Dashboard open Configure (top right).
- Open Policies and profiles section.
- Search for the default profile named GOOGLE APPLICATION.
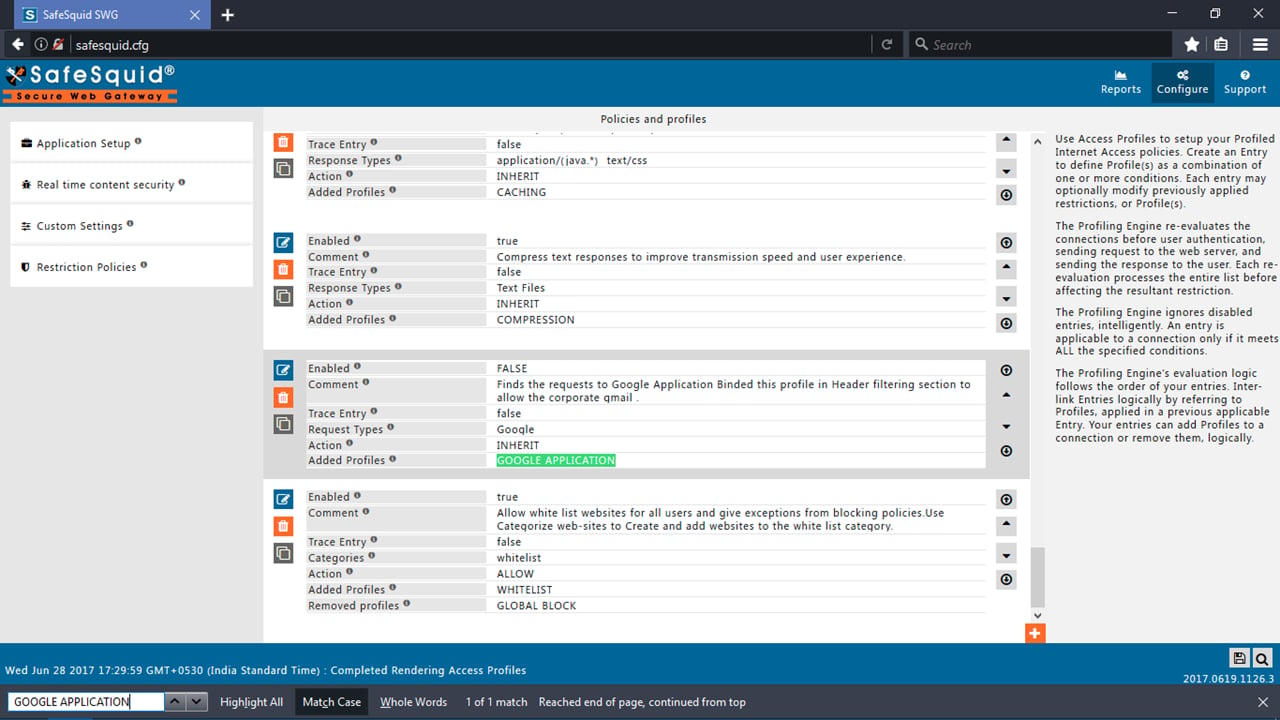
- Edit and enable this policy.
Enable policy from Header Filter section
Insert a header so only allowed domains are accepted by Google.- Open Restriction Policies (left panel).
- Open Privacy Control submenu.
- Open Header Filter section. Ensure Global is Enabled True.
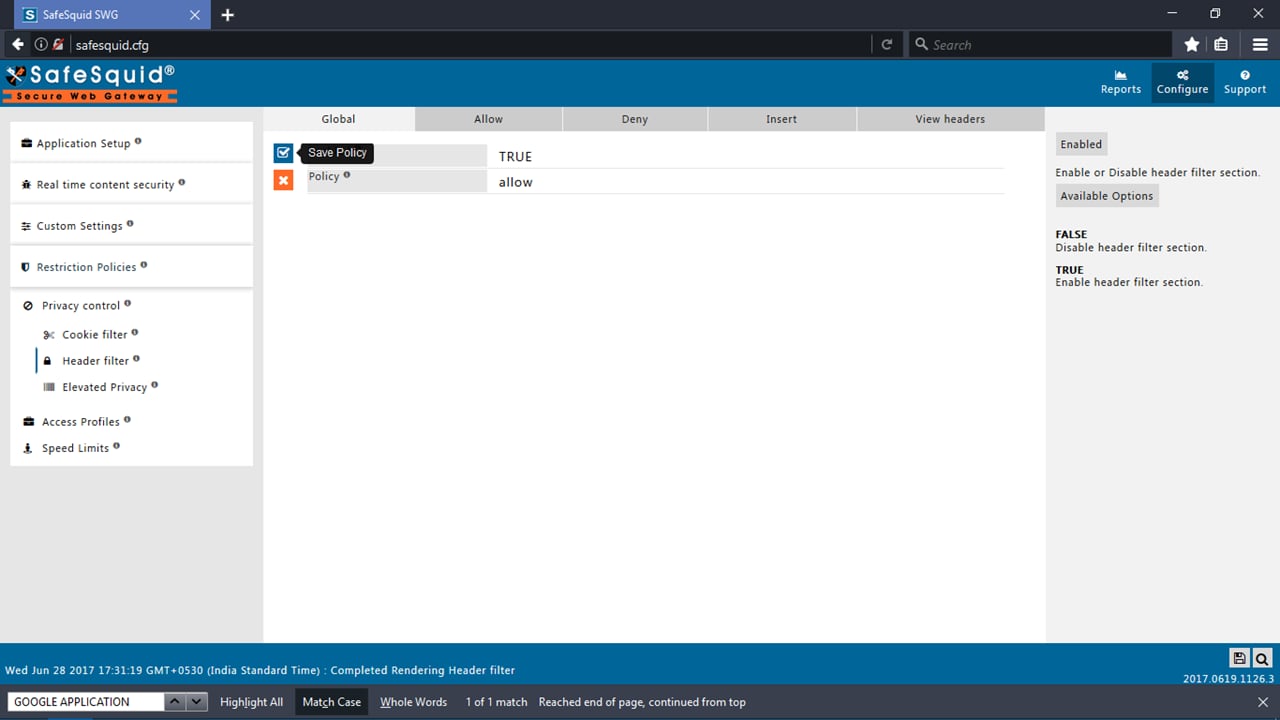
- Open Insert tab.
- Search for default profile GOOGLE APPLICATION (first rule).
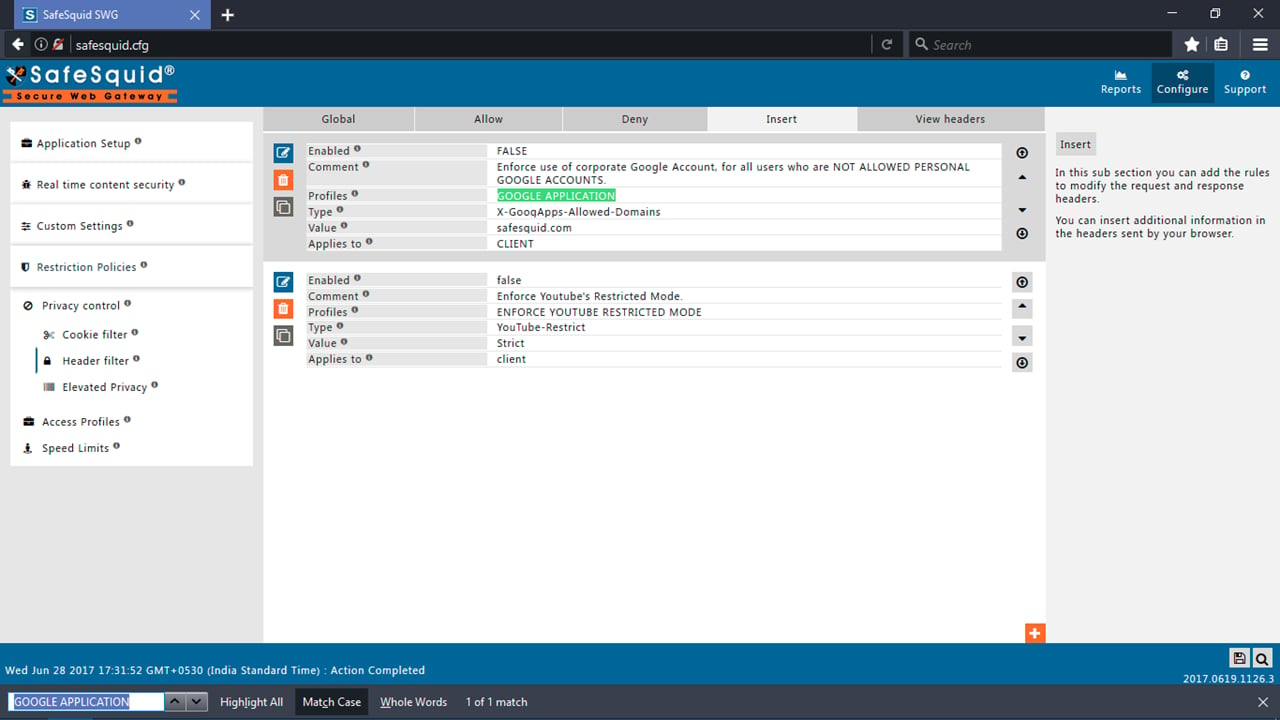
- Edit and enable this rule. Add allowed domains in the value field (comma-separated, no space). Save the policy.
Verification and Evidence
- Block test: Sign in to Google (e.g. mail.google.com) with a personal Gmail account through the proxy. Google returns an error template or message listing the allowed domains; sign-in is blocked.
- Allow test: Sign in with a corporate Google Workspace account (allowed domain). Sign-in succeeds and mail works.
- Interface: Configure → Restriction Policies → Privacy Control → Header Filter shows the GOOGLE APPLICATION Insert rule with the correct domain list. Policies and profiles shows GOOGLE APPLICATION enabled.
- Audit: Access logs and restriction logs show traffic to Google; export from the Reporting Module for evidence of policy enforcement.
Troubleshooting
Next steps
- Header Re-Write for header filtering and privacy controls.
- Access Restriction for URL and category-based policies.
- SSL Inspection for HTTPS visibility and bypass rules.