
Limit enforcement flow
Overview
TheLimits section allows administrators to constrain bandwidth, connection counts, and data transfer sizes on a per-profile basis.
Core Mechanics (C++ Source Validation)
Token-bucket rate, quota counters, request cap enforcement.- Bandwidth Shaping: SafeSquid utilizes a token-bucket mechanism. Connections are assigned to a specific
LimitGroup. The traffic shaper enforces thedownloadratethrottle globally across all connections in that group. - Quota Tracking: Global and per-user transfer quotas (
maxdbytes,maxubytes,maxrequests) are updated incrementally as payloads are flushed. Cached payloads (CONNECTION_CACHING) can be configured to bypass quota deductions (LIMIT_CACHE). - Enforcement: If a connection violates
maxrequests, the connection action is instantly set to block, serving the block template with aLMS_TOO_MANY_REQUESTSstatus and generating aTCP_DENIEDlog entry.
Schema Fields
Global Fields
- Enabled (enabled): Toggles the entire Limits subsystem on or off.
Rule-Based Fields (Per Connection Tuning)
- Enabled (enabled): Toggles the specific rule.
- Comment (comment): User description of the rule.
- Profiles (profiles): The trigger condition. The rule applies if the connection has this tag.
- Action (action): Determines whether the limit applies (
Apply) or skips/bypasses (Bypass). - Template (templ): Key template to track quotas against (e.g., grouping by client IP or username).
- Download transfer limit (maxdownloadbytes): Maximum bytes a client can download before being blocked.
- Upload transfer limit (maxuploadbytes): Maximum bytes a client can upload before being blocked.
- Request limit (maxrequests): Maximum number of HTTP requests allowed within the tracking window.
- Download rate (downloadrate): Bandwidth throttle (e.g., bytes per second) applied to downloads.
- Adjust Transfer Limits (flags): Modifier flags for how limits are enforced or tracked.
Troubleshooting
Check/var/log/safesquid/native/safesquid.log for limit enforcement messages. A client hitting a quota will typically receive a 403 Forbidden with a specific limit-exceeded template.
How SafeSquid processes the list
- On each relevant request, every enabled row matching profiles is evaluated.
- Request limit exceeded → HTTP 429 and the row Template block page (Action field is stored but not read by limits code).
- Download / upload transfer limits — remaining bytes are the tightest cap among matching rows; when remaining reaches 0, further transfer on matching connections is blocked.
- Download rate — lowest non-zero rate among matching rows wins for throttling.
- Adjust Transfer Limits flags: Limit cache transfers (count cached responses), Per-request limit (do not accumulate row counters at connection end — each request gets full quota), Group limit (share download rate bucket across matching connections).
- After connections complete, byte and request counters increment for matching rows (unless Per-request limit or cache exclusion applies); counters clear on the periodic reset.
Important entry fields
- Profiles — Limit to connections with these Access Profile tags. rules). Typical tags:
RESTRICTED DOWNLOAD TRANSFER RATES,RESTRICTED UPLOAD TRANSFER RATES. - Action — Stored in config but not read in limits code — does not change allow/deny behaviour.
- Template — Block page when Request limit is exceeded. Blank uses
blocked. Download/upload overruns use the default blocked path without this field. - Download / Upload transfer limit — Maximum bytes counted against this row since last counter reset (~10 s).
0= no cap from this row for that direction. - Request limit — Maximum requests counted since last reset.
0= unlimited. Exceeded → HTTP 429. - Download rate — Throttle in bytes/sec.
0= no rate from this row. Lowest non-zero matching rate wins. - Adjust Transfer Limits — Limit cache transfers, Per-request limit, Group limit — see processing order above.
Examples
Open Configure → Restriction Policies → Speed Limits → Set limits. Each row shows Enabled, Comment, Profiles, Action, Download/Upload transfer limit, Request limit, Download rate, and Adjust Transfer Limits.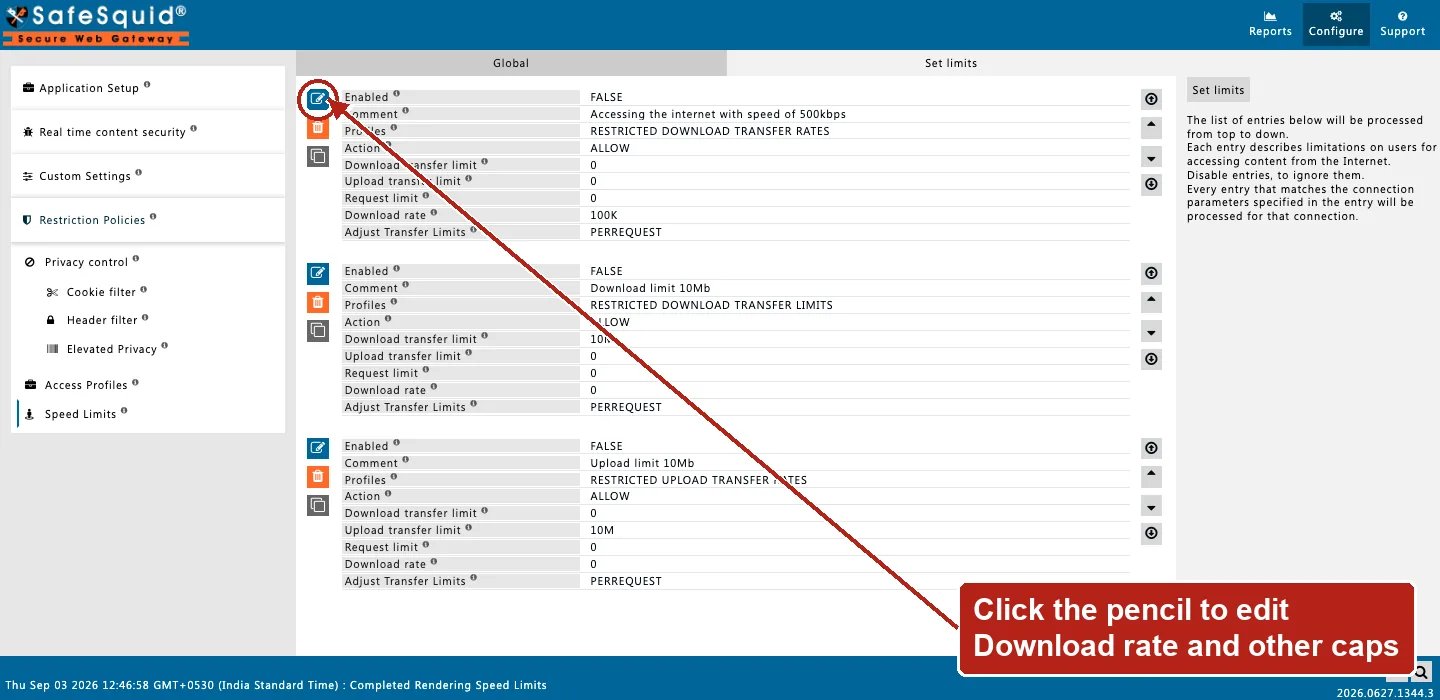
Speed Limits — Set limits rows
How to verify
- Assign a test profile and reproduce large download or many parallel requests.
- Enable LIMITS in
LOG_LEVELfor nativelimits:download/upload limit and rate lines. - Open Reports → Detailed logs; blocked transfers show
filter_namefor limits and reason such asMax Requestsor upload limit text. - Confirm counter reset behaviour by waiting ~10 seconds and retrying after hitting a window cap.