Core mechanics
Full sync — all valid servers
Each enabled valid LDAP servers row binds and runs a paged cache load in one update cycle. Maps accumulate entries from every successful server.Default @domain
First valid row’s Ldap Domain becomes the default domain. Logins without@ get @domain appended and uppercased for map keys.
Auth — first matching server
Authentication walks servers until the domain (and optional base DN) match; stops on bind success or invalid credentials.ldapgroupfilter
Stored in config but not used in search code — groups come from Group Identifier attributes and DN OUs.
LDAP cache update
Examples
Open Configure → Application Setup → Integrate LDAP → LDAP servers. Each row carries the connection fields plus Ldap Domain, Login Attributes, and Group Identifier shown here (the Ldap Password row is redacted from this capture).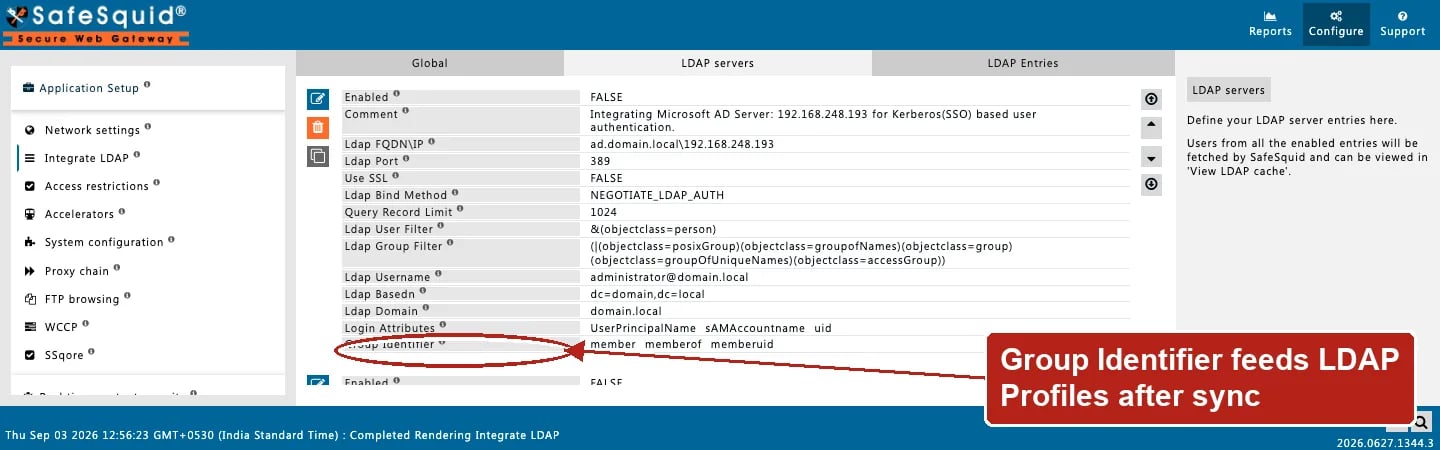
Integrate LDAP — LDAP servers row
How to verify
- Open LDAP Entries after cache thread runs.
- Enable LDAP + SECURITY logs.
- Sign in; confirm LDAP profile application in Detailed logs.